A post-quantum encrypted file vault that runs on your own server.
FortSeal locks every file on your computer before it leaves. Your server only ever holds sealed data it cannot open. End-to-end encrypted. The FIPS build runs on the AWS-LC FIPS 140-3 validated module, built for law firms, defense contractors, and any team that must keep custody of its own files.
Built for CUI, ITAR, and CMMC
The FIPS build runs every cryptographic operation that protects your files inside the AWS-LC FIPS 140-3 validated module, NIST CMVP certificate #5314. On your own server, with no third-party cloud in the loop.
FIPS 140-3, level 1. Active on the NIST CMVP list until 2031. The server reports the exact module version in its health check so an assessor can match it to the certificate.
Post-quantum key establishment (FIPS 203), authenticated encryption with module-generated IVs, PBKDF2 and HKDF, SHA-256. All approved services of the module. Full list on the security page.
Control-by-control mapping for CMMC 2.0 Level 2, with the three exceptions named. Nothing here is a certification: the module is validated, FortSeal uses it.
What you get
Sealed on your machine
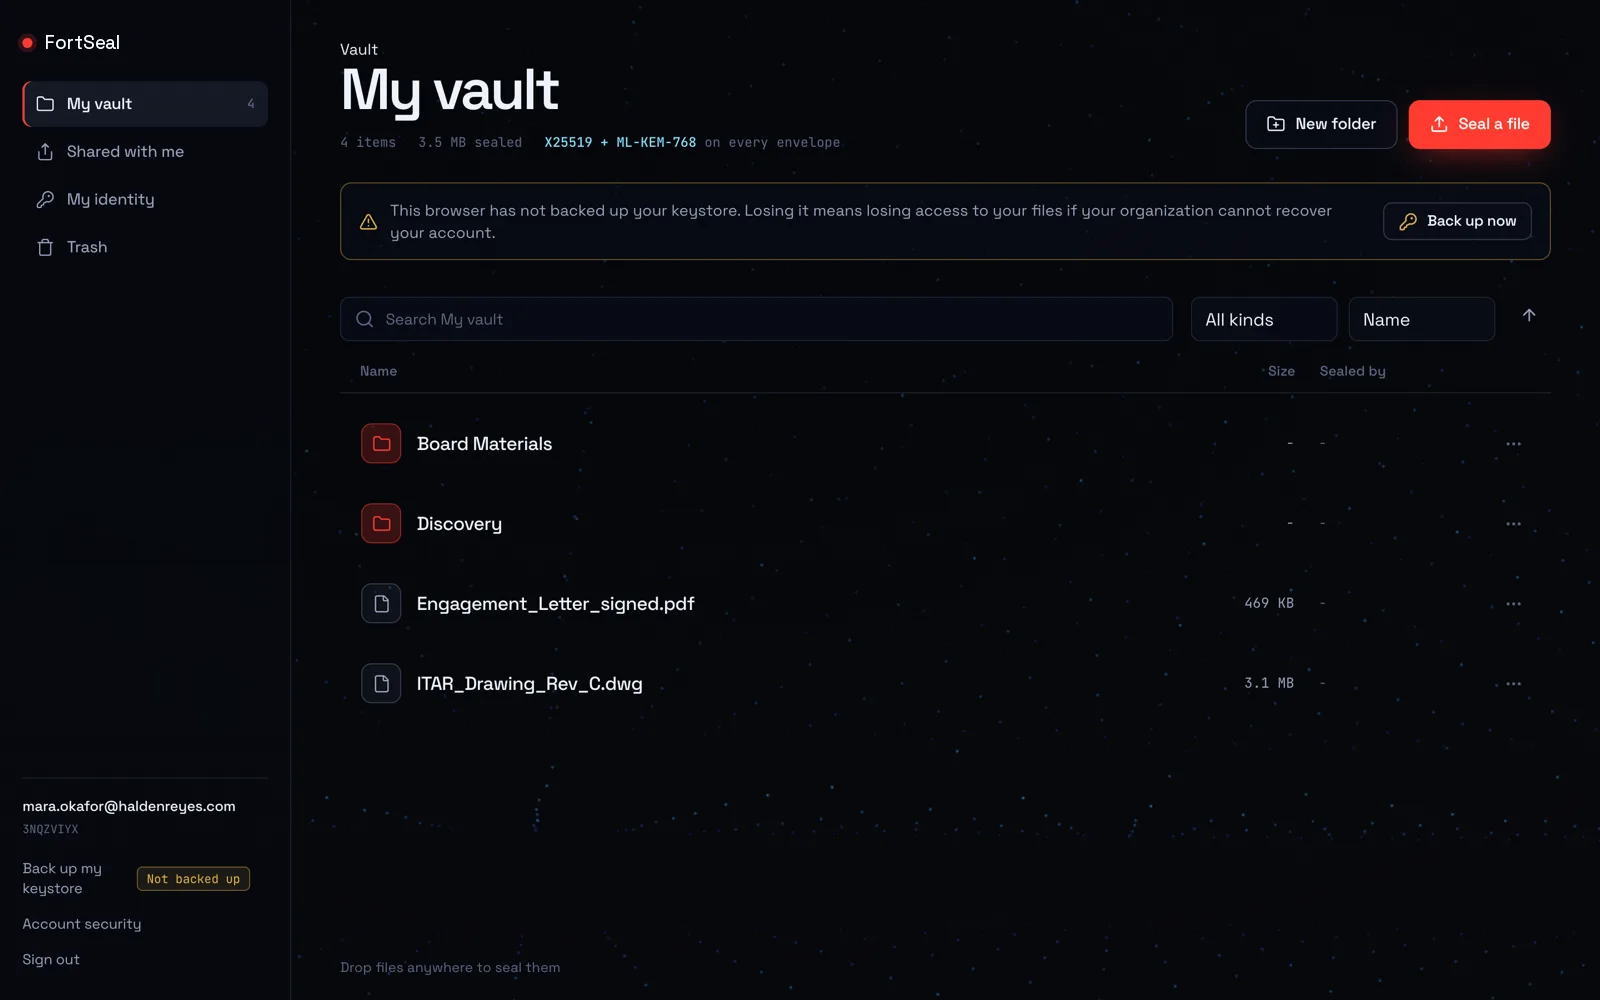
Files are locked before they leave your computer. The server only ever stores sealed data.
Runs on your server
On-prem deployment, an offline signed license, no third-party cloud in the loop.
Built for teams
Sharing, an admin console, SSO and SCIM, an audit log, and 2-of-3 org recovery.
Who it is for
Law firms
Privileged documents and discovery sets that can never sit on a drive you do not control. Staff stop emailing PDFs to themselves.
Defense contractors
Export-controlled drawings and CUI that must stay on your own metal, with a record of who touched what.
Teams that own their data
If policy says no third-party cloud, this is the file sharing your people will actually use instead of USB sticks.
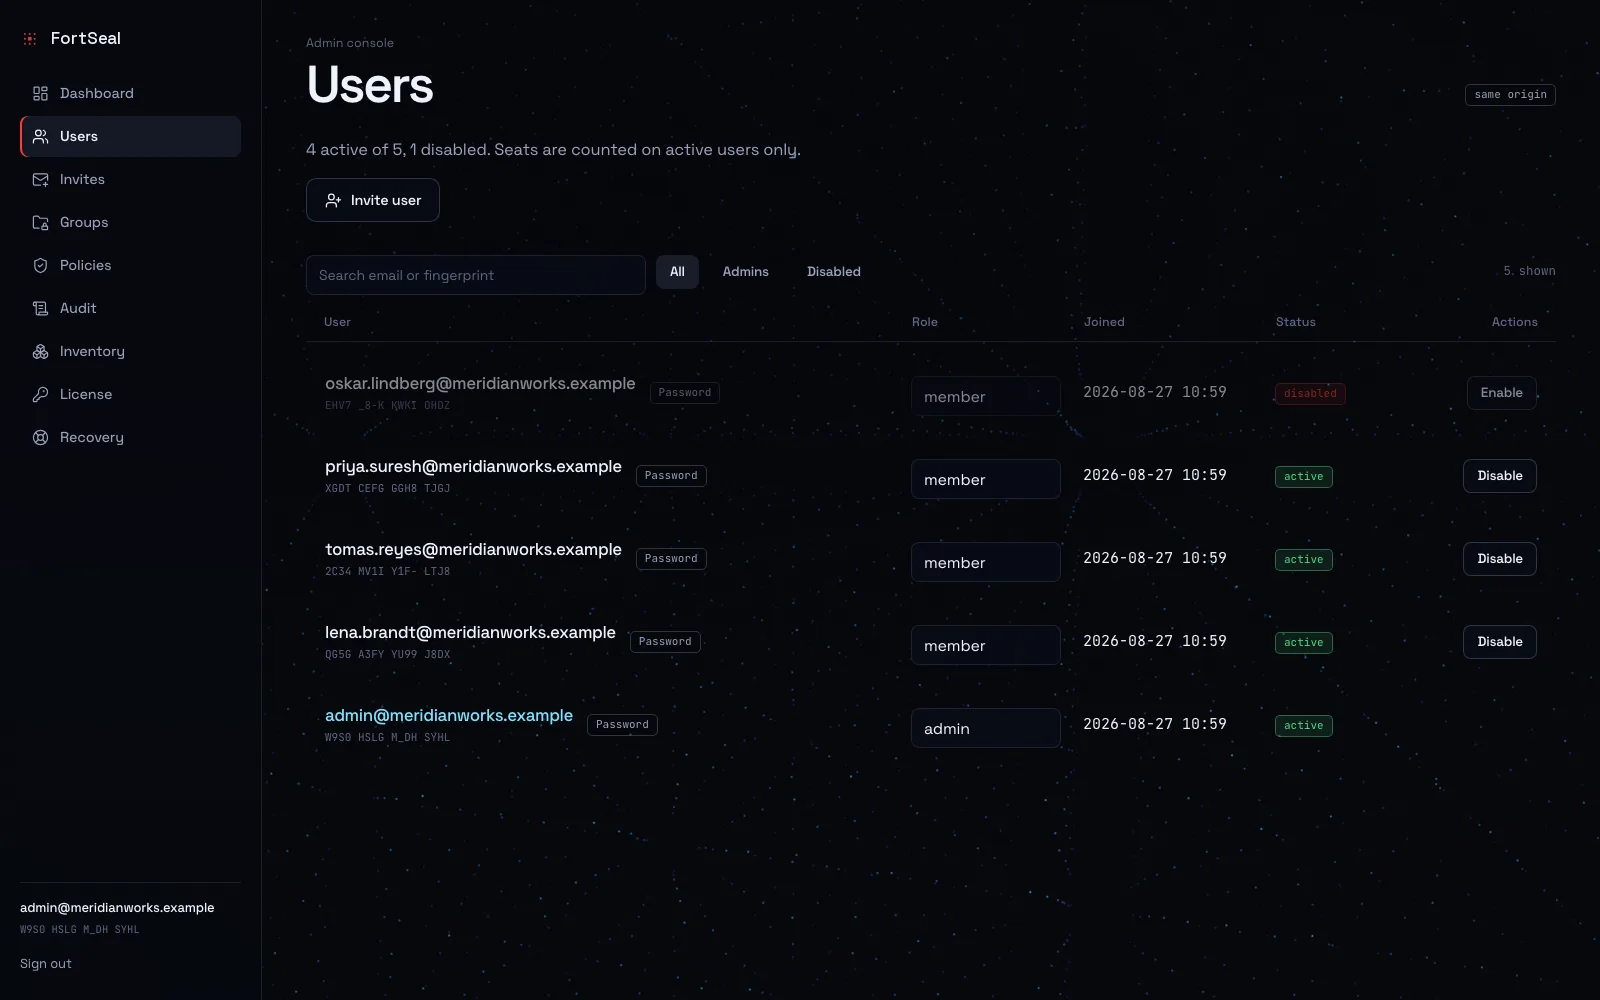
Admin console: users, seats, license, audit.
What the server stores
Your team sees
- quarterly-report.pdf
- client-agreement-v3.docx
- drawing-set-rev-c.dwg
- discovery-batch-04.zip
- org-chart.xlsx
Your server sees
- 7f3a91c4e2d0… (2,318 bytes, sealed envelope)
- 91be04f8aa17… (1,904 bytes, sealed envelope)
- e2d09a3355c0… (480,412 bytes, sealed blob)
- 4c77f81be6d9… (3,250,118 bytes, sealed blob)
- a0d51fc2907b… (53,687,091 bytes, sealed blob)
Every name, every byte of content, and every key is sealed on the client with a post-quantum envelope before upload. See how the sealing works.
FortSeal vs. the others
"Others" means the cloud file-sharing services most teams use today. Some of them encrypt end to end; almost none run on your hardware, and we know of none that seal files with a post-quantum key exchange.
Questions buyers ask
- What is post-quantum encryption, and why does a file vault need it?
- Post-quantum encryption uses algorithms a future quantum computer cannot break. Traffic recorded today can be decrypted years from now if it relied on classical key exchange alone. FortSeal seals every file with a hybrid X25519 + ML-KEM-768 key exchange (NIST FIPS 203) and AES-256-GCM, so recorded ciphertext stays worthless.
- Does FortSeal use FIPS 140-3 validated cryptography?
- The FIPS build runs every cryptographic operation that protects your files inside the AWS-LC FIPS 3.1.0 module, NIST CMVP certificate #5314 (FIPS 140-3, level 1). The module is validated and FortSeal uses it; the server reports the exact module version in its health check so an assessor can match it to the certificate.
- Does it help with CMMC 2.0, NIST SP 800-171, ITAR or CUI?
- Yes. The compliance page maps every NIST SP 800-171 Rev 2 control to implemented, partial, or yours, with 3.13.11 (FIPS-validated cryptography for CUI) supported in the FIPS build and the three exceptions named. Files never leave hardware you control, which is the structural fact ITAR and CUI programs need.
- Can FortSeal, or anyone running it, read my files?
- No. Files are sealed on your computer before upload, and your server stores only sealed data. We hold no files and no keys, so a vendor breach or subpoena exposes nothing. That also means we cannot reset a password: recovery is 2-of-3 shares held by your own people.
- Does it work air-gapped, without any cloud account?
- Yes. FortSeal runs on your own server with an offline, signed license file. There is no phone-home, no third-party cloud, and no connection required to keep working.
- What does an on-prem encrypted file vault cost?
- A seat is one user account, and there is no minimum. Team is $60 per seat per month; from 25 seats every seat drops to $40 per month. Enterprise is $60 per seat per month, or $90k per year per instance with unlimited seats. One tier, everything included: sharing, admin console, SSO and SCIM, audit log, organization recovery.
Pricing
Team
We cannot read your files. We cannot reset your password. Losses without a backup are permanent.